[Column] MalaysiaKini: Power, water, oversight: Malaysia’s data centre boom needs stronger rules
© 2026 Suppiah & Partners. All rights reserved. The contents of this newsletter are intended for informational purposes only and do not constitute legal advice.
by Thulasy Suppiah, Managing Partner
MALAYSIA has recently undergone a significant shift in its legal approach to bullying and cyberbullying, driven largely by public outrage over tragic losses of life. The most notable result is Section 507D(2) of the Penal Code—widely dubbed the “Esha Clause.”
This provision criminalises threatening, abusive or insulting conduct intended to provoke a person to harm themselves or another person, or that the perpetrator knew or ought to have known was likely to do so. If that provocation results in a suicide attempt or death by suicide, the maximum prison sentence rises to ten years.
Having this law on the books sends a strong moral message. However, the public must understand the harsh legal reality: a severe penalty does not guarantee an easy conviction, nor does it act as an immediate shield for victims.
In a criminal court, proving that bullying took place may only be half the battle. The ongoing investigation into the tragic death of 14-year-old Keziah Nisha may become an important test of this clause.
While police are presently investigating the case under Section 507B, the investigation remains active and no final charging decision has been announced. It would therefore be premature to conclude that Section 507D (2) has been ruled out.
Nevertheless, the case highlights the immense difficulty at the heart of the Esha Clause. Prosecutors must prove not merely that the conduct was cruel or distressing, but that the accused intended to provoke self-harm or knew or ought to have known that the conduct was likely to do so. Where suicide followed, they must also prove that it occurred as a result of that provocation. Human distress rarely has a single, tidy cause. Where mental health, accumulated incidents, and other pressures overlap, establishing that connection beyond a reasonable doubt becomes a monumental hurdle.
But there is a deeper limitation to the Esha Clause. It is fundamentally an after-the-fact tool. It can hold a perpetrator accountable after threatening or abusive conduct has occurred, but it cannot by itself provide the immediate protection a vulnerable person may urgently need.
Criminal law can punish and deter, but it cannot substitute for protecting a victim in real time. Although the Esha Clause applies regardless of the victim’s age, its limitations are especially serious when children are involved. Children depend heavily on parents, teachers and school administrators to recognise the danger and intervene before bullying escalates into self-harm.
True protection therefore depends on what happens during the critical hours and days after a child first reports bullying or shows signs of distress. Yet Malaysia has moved from fragmented legal protections to an increasingly crowded anti-bullying framework. Beyond the Penal Code, we now have the Online Safety Act and the Anti-Bullying Act 2026, which established the Tribunal for Anti-Bullying.
While these measures serve different purposes, making sense of them in the midst of a crisis can be daunting. Teachers and school administrators must currently navigate the 2023 bullying guidelines, the sweeping 402-page 2026 Safe School Management Guidelines, the separate Student Protection Policy, the SAFE framework, and procedural reporting timelines such as SOP 1:3:7.
Having multiple laws and thick policy documents is not the same as having a cohesive safety net. When a child is facing severe psychological distress, a terrified parent or an overwhelmed teacher does not have time to solve an administrative puzzle. They need a single, unambiguous “no-wrong-door” emergency triage protocol. This must include an immediate suicide risk assessment, interim protection, and a designated response coordinator.
The Esha Clause is necessary, but it is not a safety net. The true measure of our national anti-bullying framework should not be how severely we can punish a perpetrator after the fact, but whether we can protect a victim in time. If a child facing bullying has attempted suicide or is already gone, our frontline intervention system has failed to reach that child in time. To truly honour Esha and the other victims who inspired these reforms, early intervention must become our first and most urgent line of defence.
Written By:
Thulasy Suppiah,
Managing Partner,
Suppiah & Partners,
UG-13, Lexa Galleria, 45, Jalan 34/26,
Wangsa Maju, 53300 Kuala Lumpur.
Handphone no: 012-4915238
© 2026 Suppiah & Partners. All rights reserved. The contents of this newsletter are intended for informational purposes only and do not constitute legal advice.
by Thulasy Suppiah, Managing Partner
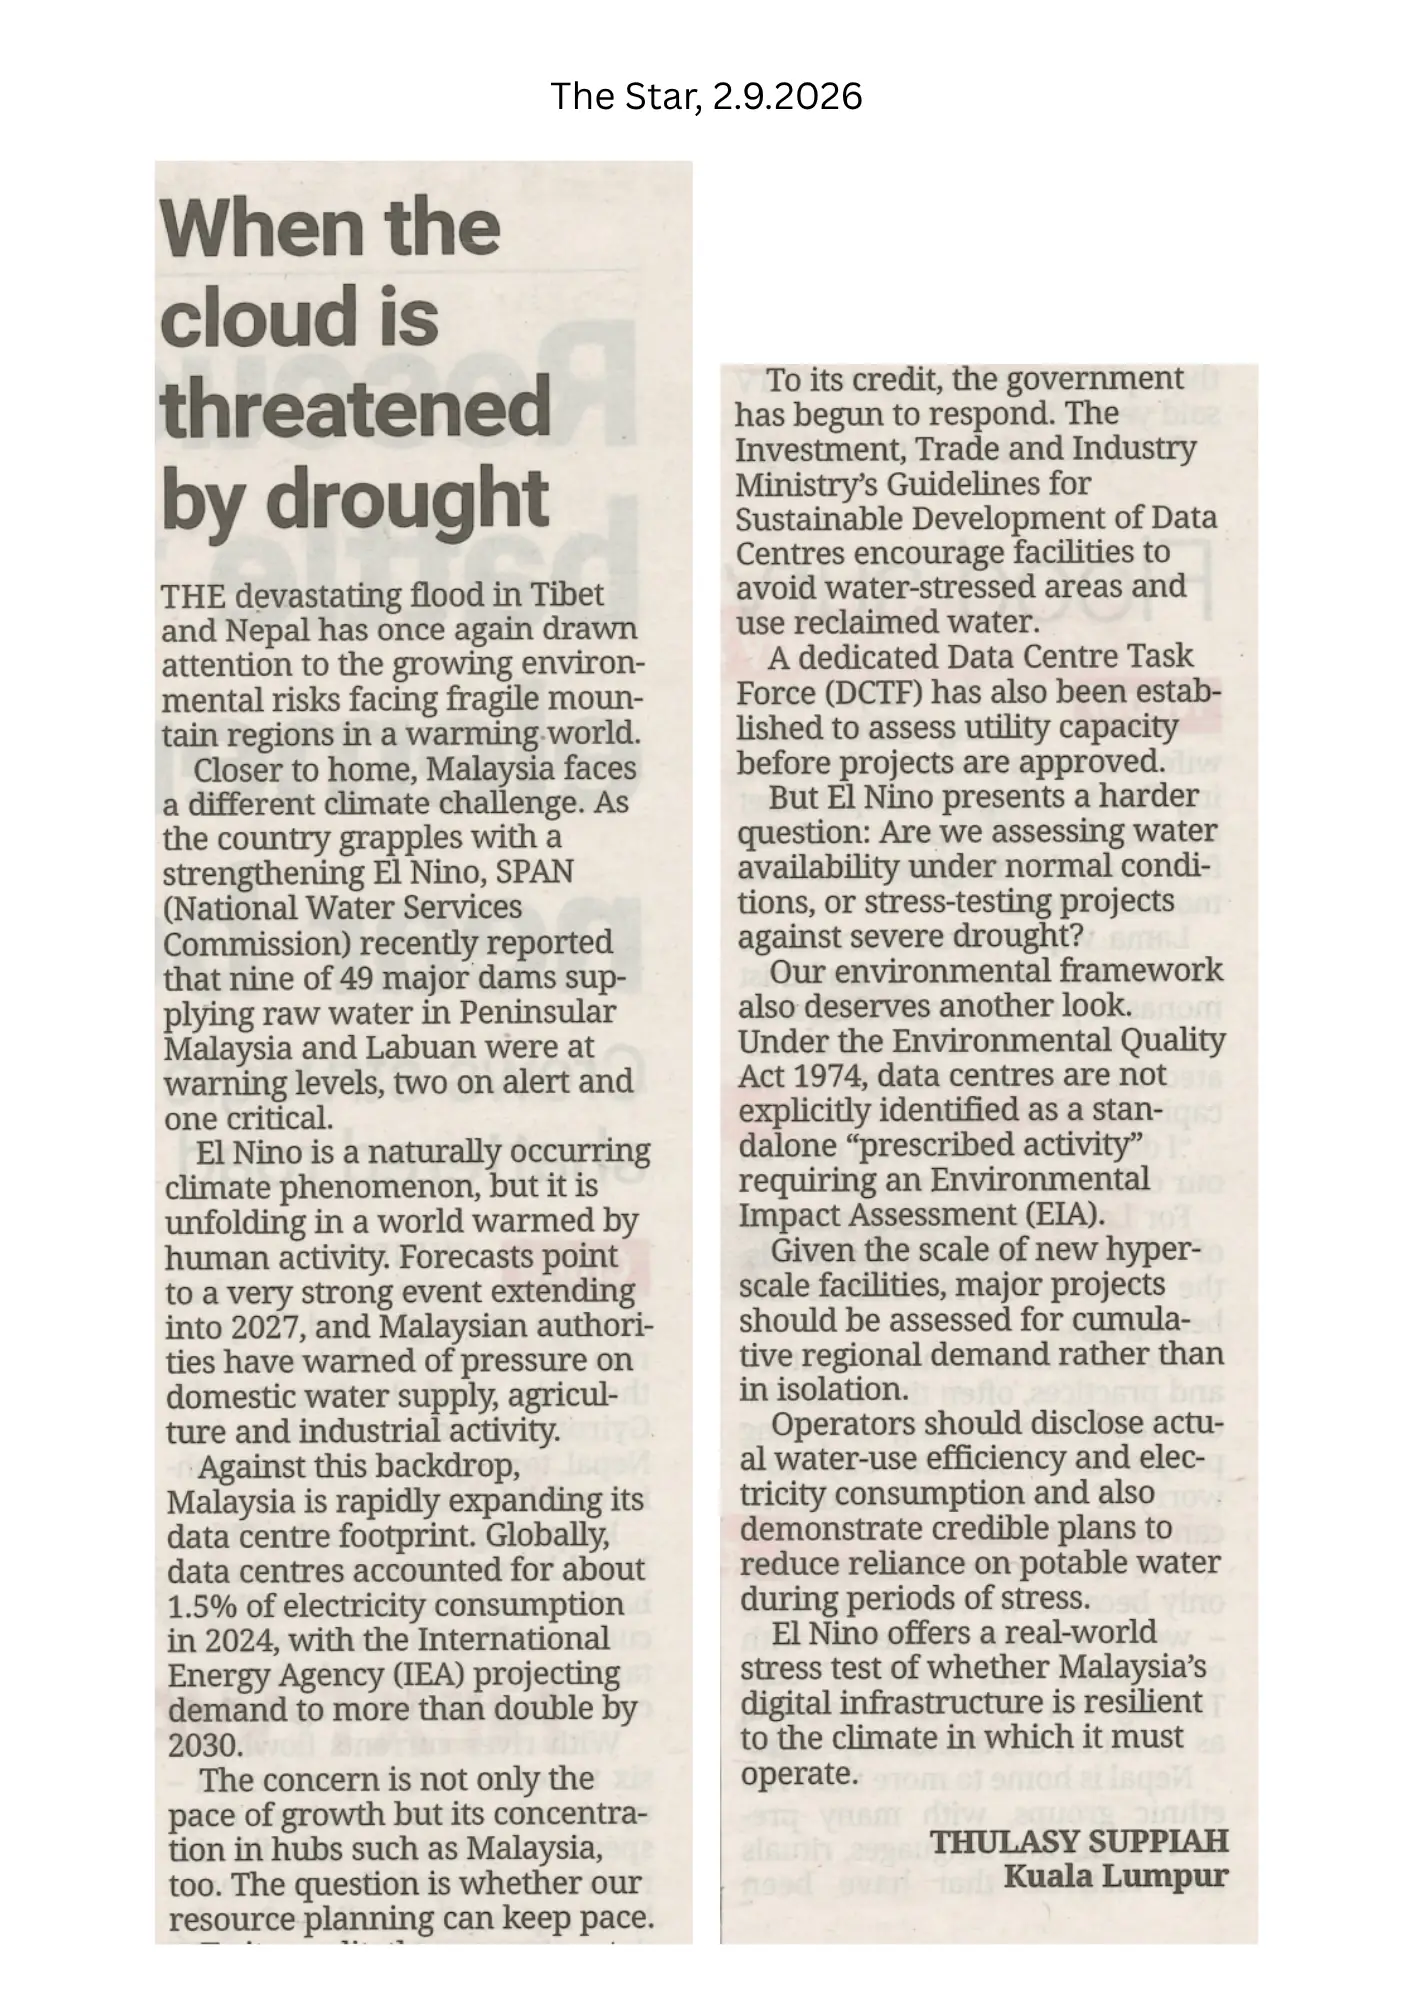
THE devastating flood in Tibet and Nepal has once again drawn attention to the growing environ-mental risks facing fragile moun-tain regions in a warming world.
Closer to home, Malaysia faces a different climate challenge. As the country grapples with a strengthening El Nino, SPAN (National Water Services Commission) recently reported that nine of 49 major dams sup-plying raw water in Peninsular Malaysia and Labuan were at warning levels, two on alert and one critical.
El Nino is a naturally occurring climate phenomenon, but it is unfolding in a world warmed by human activity. Forecasts point to a very strong event extending into 2027, and Malaysian authori-ties have warned of pressure on domestic water supply, agricul ture and industrial activity.
Against this backdrop, Malaysia is rapidly expanding its data centre footprint. Globally, data centres accounted for about 1.5% of electricity consumption in 2024, with the International Energy Agency (IEA) projecting demand to more than double by 2030.
The concern is not only the pace of growth but its concentra-tion in hubs such as Malaysia, too. The question is whether our resource planning can keep pace.
To its credit, the government has begun to respond. The Investment, Trade and Industry Ministry’s Guidelines for Sustainable Development of Data Centres encourage facilities to avoid water-stressed areas and use reclaimed water.
A dedicated Data Centre Task Force (DCTF) has also been estab-lished to assess utility capacity before projects are approved.
But El Nino presents a harder question: Are we assessing water availability under normal condi-tions, or stress-testing projects against severe drought?
Our environmental framework also deserves another look. Under the Environmental Quality Act 1974, data centres are not explicitly identified as a stan-dalone “prescribed activity” requiring an Environmental Impact Assessment (EIA).
Given the scale of new hyper-scale facilities, major projects should be assessed for cumula-tive regional demand rather than in isolation.
Operators should disclose actu-al water-use efficiency and electricity consumption and also demonstrate credible plans to reduce reliance on potable water during periods of stress.
El Nino offers a real-world stress test of whether Malaysia’s digital infrastructure is resilient to the climate in which it must operate.
Written By:
Thulasy Suppiah,
Managing Partner,
Suppiah & Partners,
UG-13, Lexa Galleria, 45, Jalan 34/26,
Wangsa Maju, 53300 Kuala Lumpur.
Handphone no: 012-4915238
© 2026 Suppiah & Partners. All rights reserved. The contents of this newsletter are intended for informational purposes only and do not constitute legal advice.
As we mark 69 years of independence, Merdeka must be understood not merely as a historical milestone from 1957, but as an ongoing, living project. While we have long secured our political sovereignty, our journey toward true social and economic independence remains unfinished.
This divide is starkly visible in our daily lives. In digital spaces, public debates too often devolve into categorising citizens by race, casually reducing individuals to a “Type.” This digital tribalism proves that the colonial legacy of “divide and rule” has simply mutated, finding new life in algorithms, anonymity, and manufactured outrage.
Recent investigations and data paint a deeply concerning picture of these fractures across three critical areas:
In employment, a study by the Centre for Governance and Political Studies (Cent-GPS) demonstrated that job applicants face drastically skewed callback rates based on ethnicity despite having identical qualifications.
In housing, research by Architects of Diversity (AOD) revealed that nearly half of Klang Valley rental listings impose racial criteria, forcing marginalised tenants to pay a “discrimination tax” in higher rents just to secure a home.
In our digital discourse, an undercover investigation by media platform The Fourth exposed how social hostility is often not organic, but manufactured. Irresponsible parties fund hidden agencies, cybertroopers, and comment seeders to artificially amplify polarising talking points, creating a false illusion of widespread communal division.
These practices persist due to a glaring legislative and regulatory vacuum. We currently have a crucial window of opportunity to begin addressing these structural flaws.
In housing, as the government finalises the Residential Tenancy Bill, it is imperative that lawmakers include explicit anti-discrimination clauses. Enacting tenancy reform without addressing racial screening merely treats the symptoms of an unfair market while ignoring its root cause. We cannot claim to legislate fairness if we leave legal loopholes for unjust exclusion.
In employment, private corporations must move beyond performative diversity statements and institutionalise objective hiring safeguards, such as blind recruitment processes that evaluate candidates solely on professional merits before personal demographics are revealed.
In our digital sphere, regulatory frameworks must evolve to demand strict transparency for funded online campaigns, ensuring the public knows when social media discourse has been artificially manufactured by shadowy actors.
Yet, there is profound reason for optimism. Divisive rhetoric is steadily losing its grip on the younger demographic. Young Malaysians—born into a hyper-connected world—are increasingly recognizing that the shared struggles of stagnant wages, housing affordability, and economic uncertainty do not discriminate by race, looking past the manufactured narratives designed to compartmentalise them.
Away from the political arena and the extremes of social media, the authentic Malaysian experience has always been defined by profound warmth, shared spaces, and the quiet solidarity we show one another during national crises. As we look toward our seventh decade as an independent nation, true Merdeka requires us to bridge the gap between the unity we live and the fairness we legislate.
Only by actively rejecting the practices that fracture us can we move a step closer to fulfilling the true promise of Merdeka.
Written By:
Thulasy Suppiah,
Managing Partner,
Suppiah & Partners,
UG-13, Lexa Galleria, 45, Jalan 34/26,
Wangsa Maju, 53300 Kuala Lumpur.
Handphone no: 012-4915238
© 2026 Suppiah & Partners. All rights reserved. The contents of this newsletter are intended for informational purposes only and do not constitute legal advice.
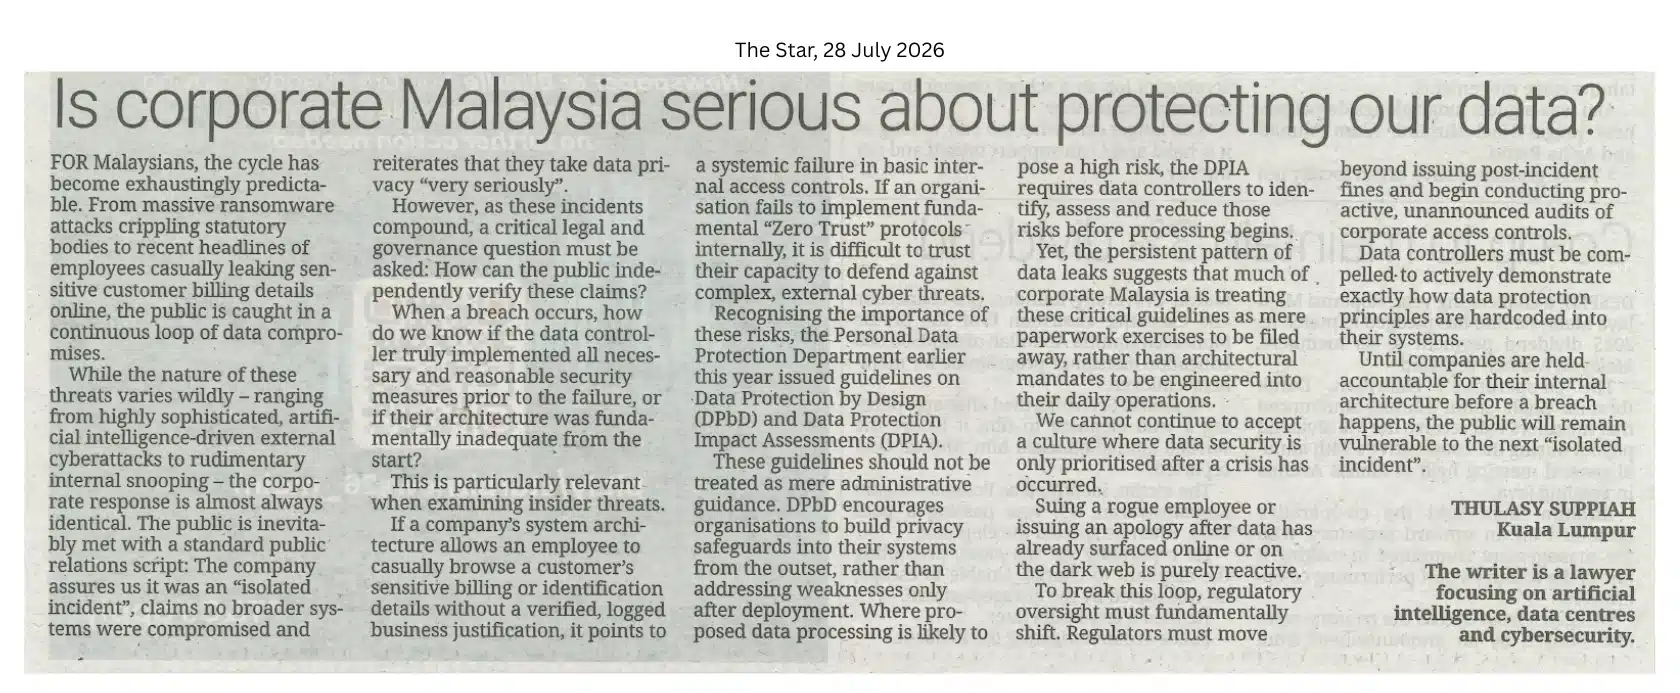
For Malaysians, the cycle has become exhaustingly predictable. From massive ransomware attacks crippling statutory bodies to recent headlines of internal employees casually leaking sensitive customer billing details online, the public is caught in a continuous loop of data compromises.
While the nature of these threats varies wildly—ranging from highly sophisticated, AI-driven external cyberattacks to rudimentary internal snooping—the corporate response is almost always identical. The public is inevitably met with a standard public relations script: the company assures us it was an “isolated incident,” claims no broader systems were compromised, and reiterates that they take data privacy “very seriously.”
However, as these incidents compound, a critical legal and governance question must be asked: How can the public independently verify these claims? When a breach occurs, how do we know if the data controller truly implemented all necessary and reasonable security measures prior to the failure, or if their architecture was fundamentally inadequate from the start?
This is particularly relevant when examining insider threats. If a company’s system architecture allows an employee to casually browse a customer’s sensitive billing or identification details without a verified, logged business justification, it points to a systemic failure in basic internal access controls. If an organisation fails to implement fundamental “Zero Trust” protocols internally, it is difficult to trust their capacity to defend against complex, external cyber threats.
Recognising the importance of these risks, the Personal Data Protection Department (JPDP) earlier this year issued guidelines on Data Protection by Design (DPbD) and Data Protection Impact Assessments (DPIA).
These guidelines should not be treated as mere administrative guidance. DPbD encourages organisations to build privacy safeguards into their systems from the outset, rather than addressing weaknesses only after deployment. Where proposed data processing is likely to pose a high risk, the DPIA requires data controllers to identify, assess and reduce those risks before processing begins.
Yet, the persistent pattern of data leaks suggests that much of corporate Malaysia is treating these critical guidelines as mere paperwork exercises to be filed away, rather than architectural mandates to be engineered into their daily operations.
We cannot continue to accept a culture where data security is only prioritised after a crisis has occurred. Suing a rogue employee or issuing an apology after data has already surfaced online or on the dark web is purely reactive.
To break this loop, regulatory oversight must fundamentally shift. Regulators must move beyond issuing post-incident fines and begin conducting proactive, unannounced audits of corporate access controls. Data controllers must be compelled to actively demonstrate exactly how data protection principles are hardcoded into their systems.
Until companies are held accountable for their internal architecture before a breach happens, the public will remain vulnerable to the next “isolated incident.”
Written By:
Thulasy Suppiah,
Managing Partner,
Suppiah & Partners,
UG-13, Lexa Galleria, 45, Jalan 34/26,
Wangsa Maju, 53300 Kuala Lumpur.
Handphone no: 012-4915238
© 2026 Suppiah & Partners. All rights reserved. The contents of this newsletter are intended for informational purposes only and do not constitute legal advice.
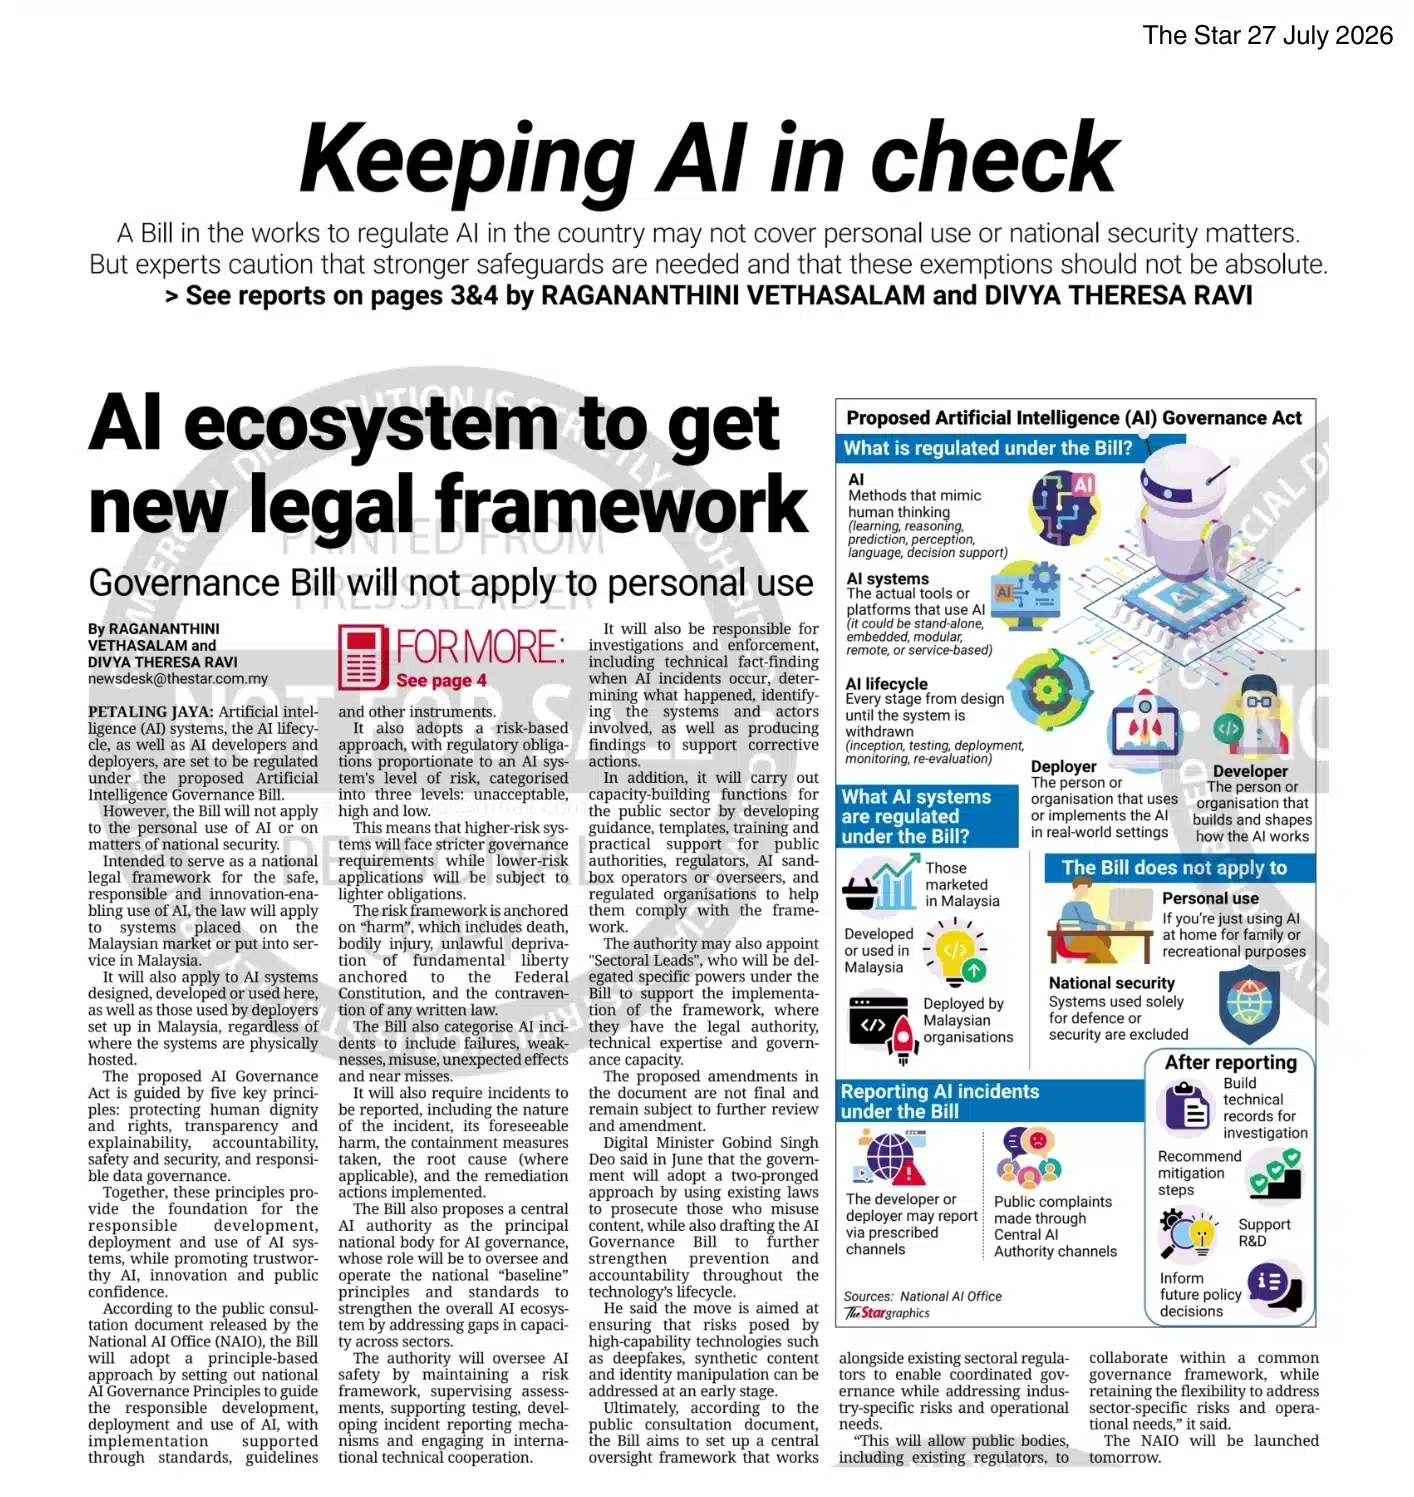
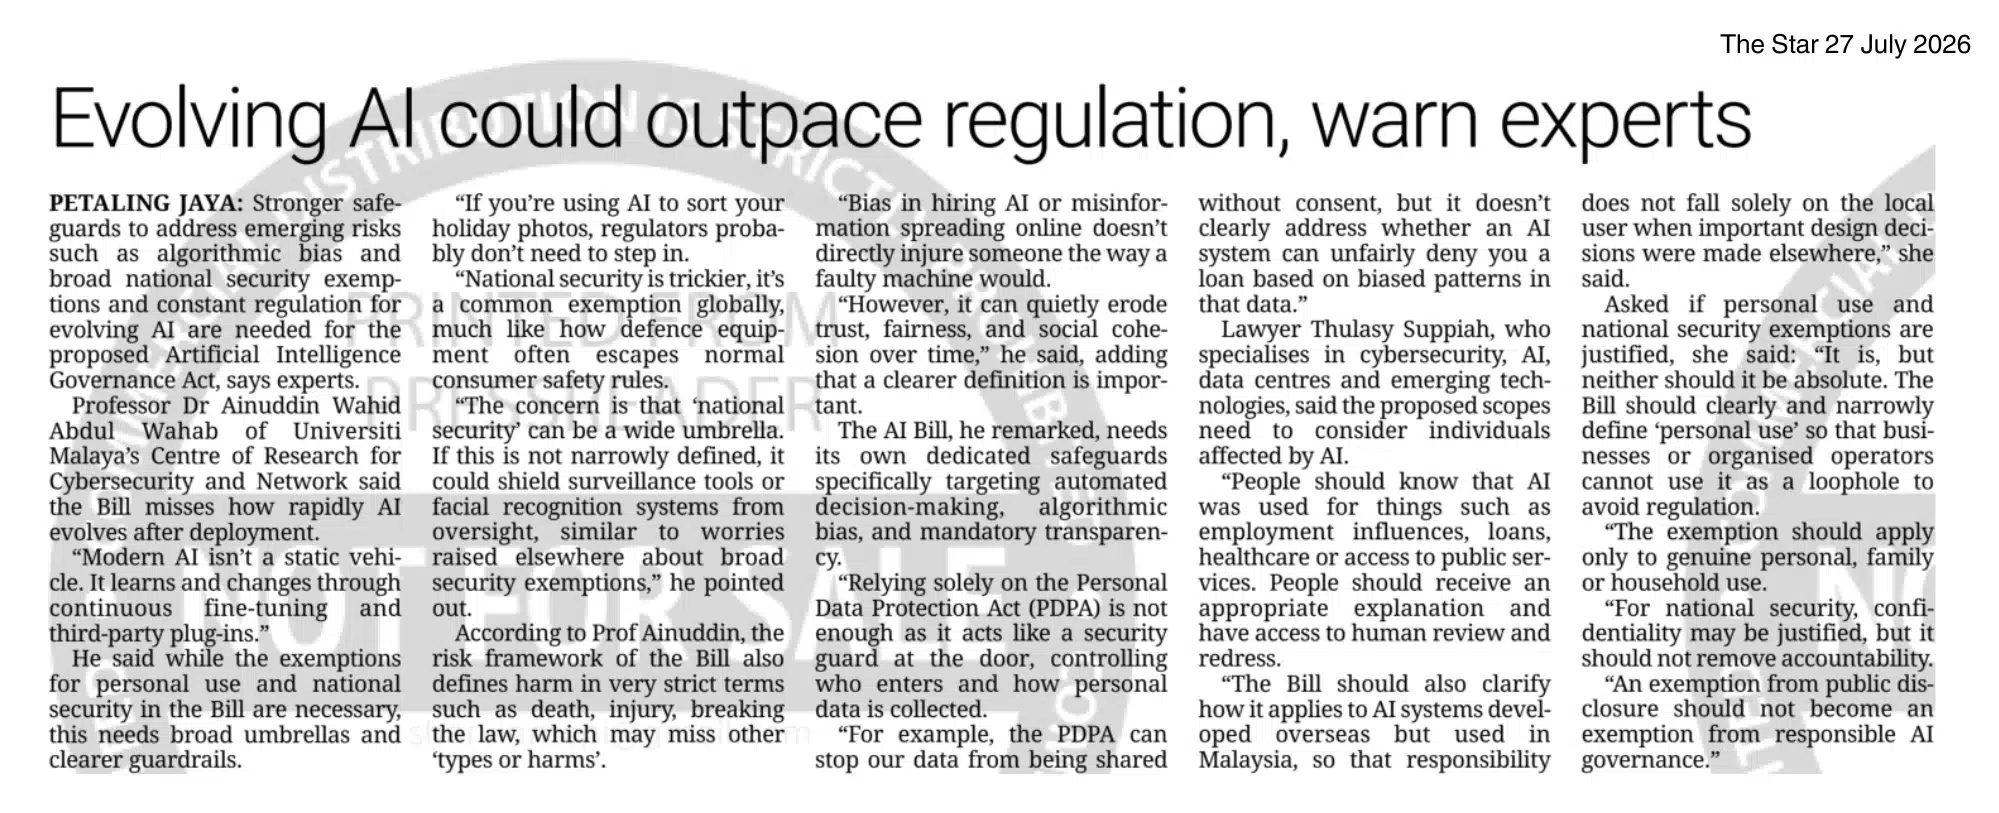
Quoted by The Star on 27 July 2026
by Ragananthini Vethasalam and Divya Theresa Ravi
© 2026 Suppiah & Partners. All rights reserved. The contents of this newsletter are intended for informational purposes only and do not constitute legal advice.
The world’s first fully autonomous attack mission using Artificial Intelligence (AI), happened in the fall of 2023. The Ukrainian Ministry of Defense officially approved the Saker Scout – an autonomous weapon system – to complete the final strike phase of a mission, completely cut off from its human handlers.
The system was developed in response to the intense electronic warfare (EW) landscape in Ukraine’s eastern Donbas region. Russian forces deployed massive jamming networks, such as the Pole-21 and Zhitel systems, which blanked out the radio and GPS signals Ukrainian drone pilots used to navigate.
The Saker Scout is a First Person View (FPV) kamikaze quadcopter drone. If heavy jamming breaks the connection to its pilot, its onboard computer-vision software fully takes over to identify, track, and detonate on military targets without human intervention.
Militaries are constantly looking for flawless partners in war, and they may have found it.
The integration of AI into military hardware has sparked a third revolution in warfare. Unlike the nuclear arms race, which relied on building expensive stockpiles, the AI arms race is defined by software, processing speed, and the mass production of cheap, autonomous systems.
By using Decision Support Systems (DSS) such as the Pentagon’s Maven Smart System integrated with advanced large language models, forces can process massive amounts of targeting data in minutes rather than days. This efficiency has triggered a global rush to develop AI-based targeting weapons, pushing global military spending to $2.88 trillion (RM 11.38 trillion) in 2025—a 41 per cent increase over the last decade.
The real-world impact of this technology was demonstrated during the recent US war against Iran. Powered by AI-driven DSS, the US hit more targets in the first four days of the campaign than it did against ISIS over an entire six-month period. In total, the US struck 13,000 targets in just 38 days, including thousands of command centres and air defences. While these systems promise unprecedented tactical results, their speed and automation raise troubling ethical questions.
Today’s arms race is uniquely destructive because cheap, asymmetric technology (like inexpensive drones) forces defenders to buy increasingly complex, multi-million-dollar countermeasures. This locks nations into an unsustainable economic spiral where billions are spent defending against cheap threats, completely freezing capital needed to solve existential global crises.
The direct diversion of capital from human welfare to weapons is a primary ethical critique of military spending as just a fraction of this, roughly USD$150 billion to USD$200 billion (RM593 billion to RM791 billion) annually, could eradicate global hunger, provide clean water, and fund universal primary education. Economists and humanitarians warn that this aggressive rearmament creates a moral deficit by diverting vital resources away from pressing global crises.
Additionally, traditional military targeting involved rooms full of human intelligence analysts manually comparing satellite photos with radio log. It’s a process that takes hours, days, or weeks. The AI compresses this OODA Loop (Observe, Orient, Decide, Act) into seconds.
When systems process data instantly, the quantity of targets skyrockets. The resulting dilemma? The logic shifts from human-driven intuition to machine-driven pattern recognition. If a human analyst is handed 500 machine-generated targets a day rather than 5, they no longer have the time to deeply question the data. This creates a severe risk of automation bias where human operators simply trust what the algorithm tells them, treating a highly complex probability estimate as an absolute fact.
Finally, the concept of faster escalation cycles due to machine-speed reactions describes a dangerous military feedback loop. When opposing militaries both deploy AI to make decisions, the speed of conflict shifts from human speed (minutes, hours, or days) to algorithmic speed (milliseconds).
What happens if one AI system misinterprets an action and reacts instantly? The opposing AI will react to that reaction just as quickly. Before human commanders can even figure out what is happening, a minor misunderstanding can spiral into a major conflict.
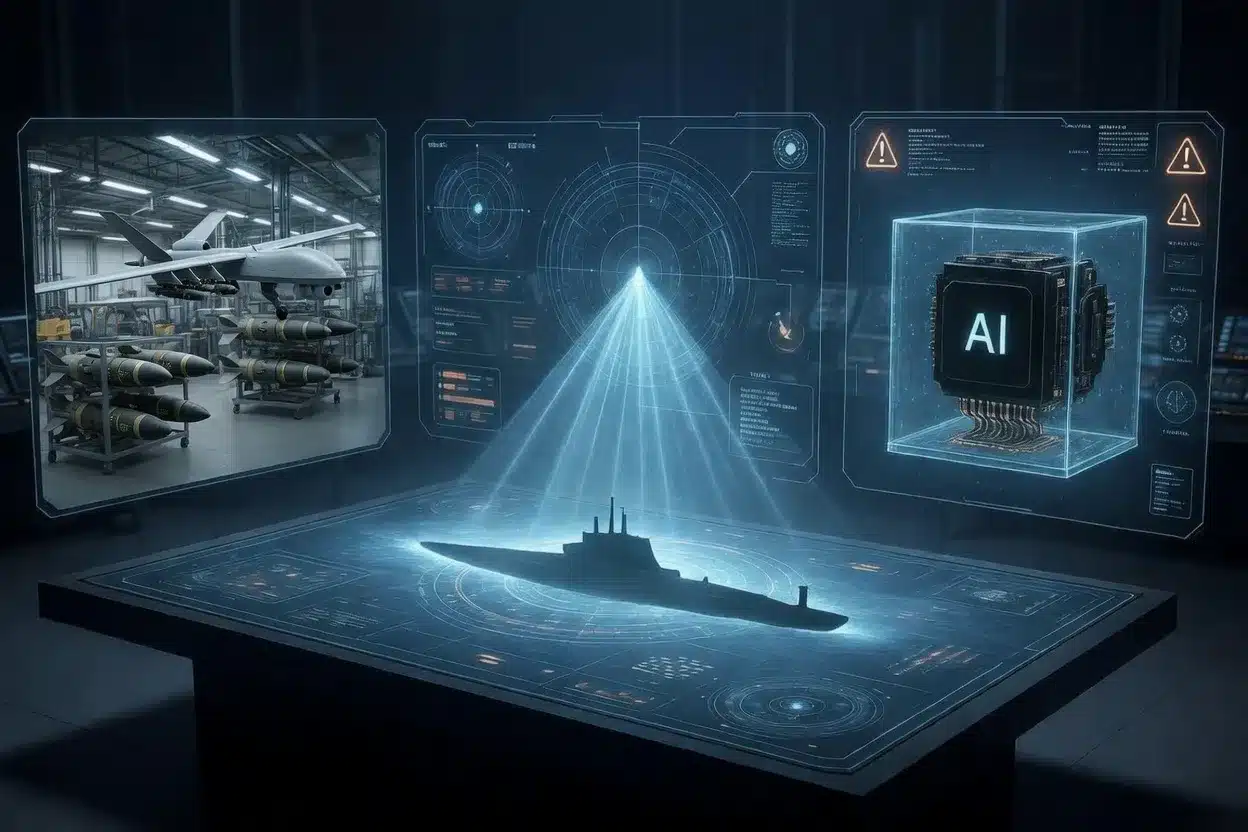
The new global AI arms race is making the world much more dangerous in three simple ways. First, it creates a stockpile problem: because AI can find thousands of targets in seconds, armies are rapidly running out of real-world missiles and drones to actually hit them. This forces factories into a frantic race to build more weapons. Second, it destabilises hidden defences: because AI can instantly map out an enemy’s hidden bases or submarines, countries feel completely exposed, forcing them to build thousands of fake decoys and extra weapons just to survive a surprise attack. Finally, it breaks peace treaties: traditional peace deals only work when you can count an enemy’s tanks or ships on a satellite map, but you cannot count or see a hidden AI computer code, making it almost impossible for nations to agree on safety rules.
Today, global stability no longer rests on how many weapons a country possesses but on who has the fastest data networks and the most aggressive code. In the current environment, every military power feels deeply exposed, creating intense, unremitting pressure to strike first before the enemy’s algorithm beats them to the punch.
As the Australian Institute of Internation Affairs noted, “A world where no one feels safe cannot be stable. It is not in the national interest of any state to create an environment of continuous arms racing and nuclear buildup.”
AI tools (especially open-source models and commercial drones) make it easier for smaller states – or even non-state actors, to develop meaningful military capabilities. This has caused a cost asymmetry advantage. Across the region, inexpensive drones and missiles are forcing the US and its Gulf partners to expend their most sophisticated, high-cost air defences.
While an Iranian Shahed-136 one-way attack drone costs a mere USD$20,000 to USD$50,000 (RM79,092 to RM197,730), intercepting it frequently requires multi-million-dollar munitions. A single Patriot interceptor costs roughly USD$4 million (RM15.82 million), while a THAAD missile ranges from USD$12 million to USD$15 million (RM47.46 million to RM59.32 million). That over 200 Ukrainian specialists are now advising the US military on how to intercept Iran’s Shahed drones without firing Patriot missiles that cost 200 times more, proves that the era of modern drone warfare has arrived – and the US is lagging behind.
Iran does not just use these weapons directly; it exports the low-tech blueprints, commercial components, and localised manufacturing capabilities to non-state proxies like the Houthis in poverty-stricken Yemen and militias in Iraq. Using Iranian-supplied, low-cost drone and anti-ship missile kits, the Houthis successfully disrupted global shipping lanes for years.
Iran is also able to frequently bypass sanctions because the components they require are entirely civilian. Recent intelligence disclosures showed the Islamic Revolutionary Guard Corps (IRGC) using front companies in global trade hubs to procure commercial Chinese satellite communication gear and antenna accessories.
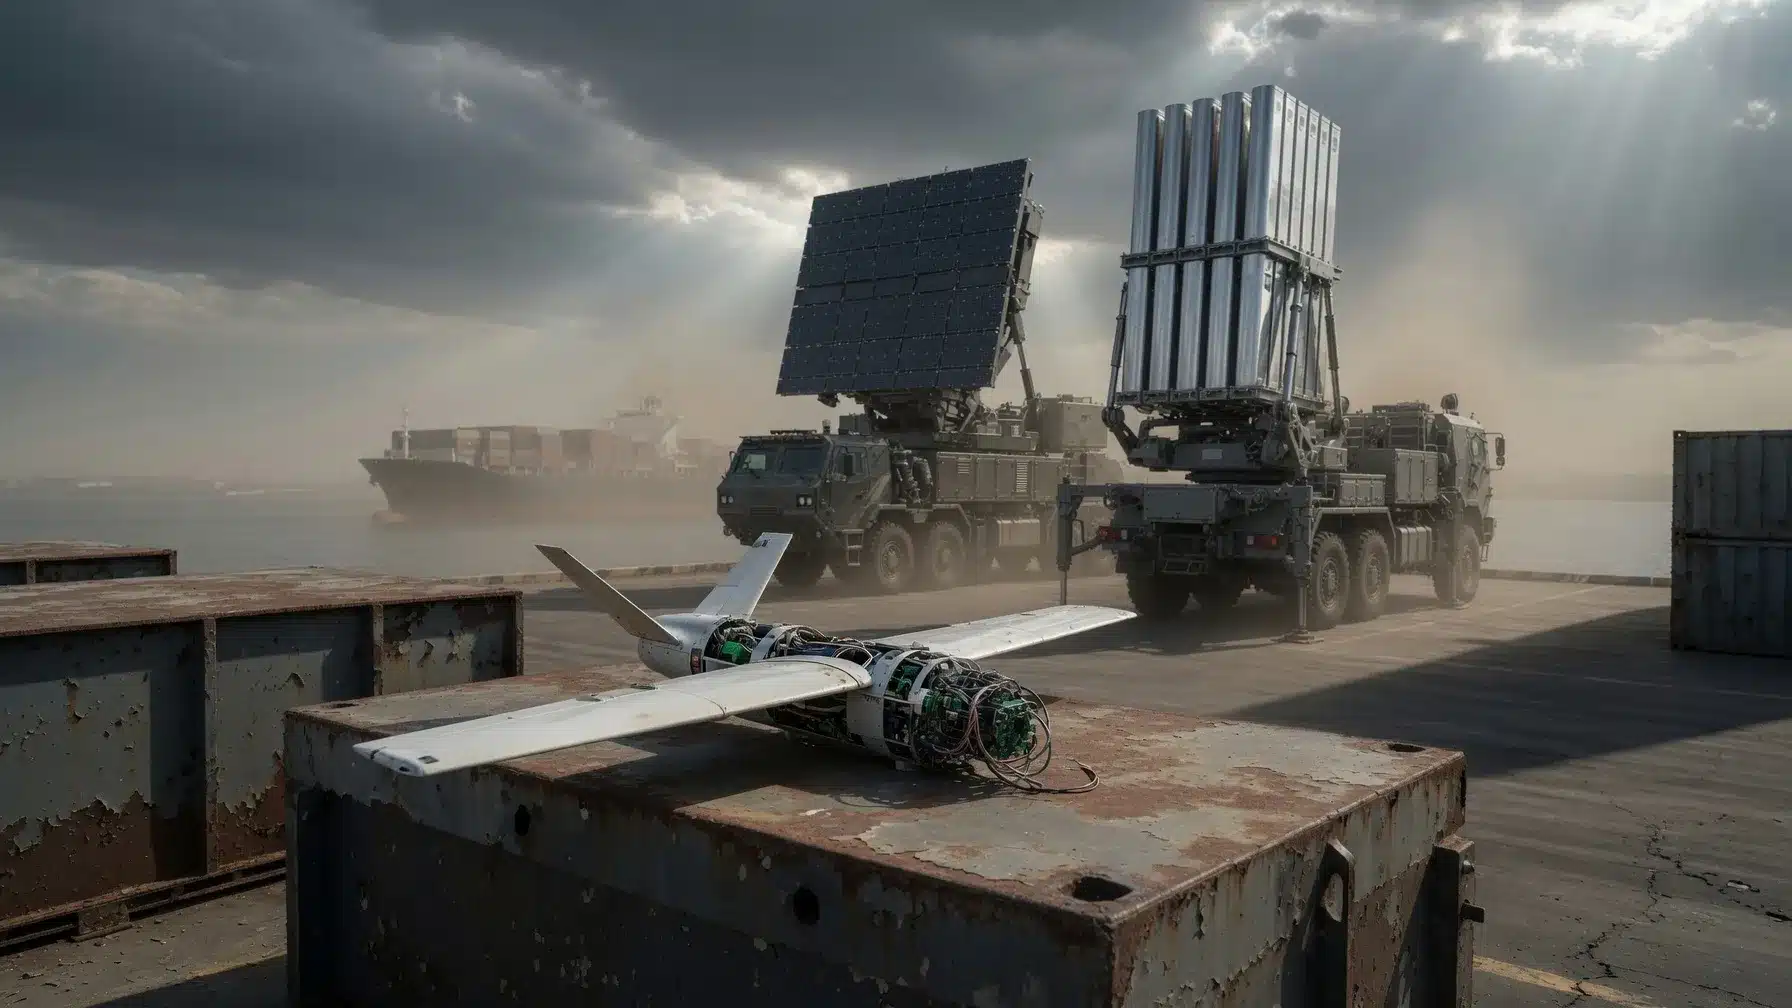
By integrating commercial guidance systems with open-source machine learning models, Iran can upgrade unguided rockets into precision-guided weapons without needing a multi-billion-dollar military-industrial complex.
AI in warfare reshapes the global balance in ways that sometimes place smaller or developing countries at an advantage. However, top-tier AI systems still require infrastructure, talent, and data – areas dominated by countries like the United States, Russia and China.
Automated cyberattacks have eliminated human fatigue by operating continuously at scale, requiring only a single success to breach networks at zero cost to attackers. This dynamic severely disadvantages smaller economies. They lack the budget and expertise to counter autonomous algorithms that scan public infrastructure and exploit flaws faster than human defenders can patch them. A striking precedent occurred between December 2025 and February 2026, when a lone hacker bypassed the safety filters of commercial models like Claude Code and GPT-4 to deploy over 5,000 automated commands against Mexico. This single AI-driven campaign rapidly exfiltrated 150 gigabytes of data, compromised the identities of 195 million citizens, and breached the federal tax authority, to prove that outdated state networks are utterly unable to cope with the velocity of modern AI intrusions.
Critical infrastructure like banks, power grids, and satellite communications increasingly relies on interconnected third-party software. This leaves less-protected nations with systemic exposure. While a fully autonomous, purely AI-generated supply-chain attack has not yet been publicly documented, a landmark precedent exists: the 2017 NotPetya cyberattack. State-sponsored hackers hijacked a mandatory Ukrainian accounting software update (M.E.Doc), and unleashed a destructive data-wiping worm. Within hours, the infection spread globally via interconnected corporate networks. It crippled shipping giant Maersk, froze multinational logistics and pharmaceutical systems, and disabled radiation monitoring at Chernobyl. It resulted in USD$10 billion (approximately RM39.7 billion) in global damages.
NotPetya remains the most destructive cyberattack in history and offers a terrifying blueprint if augmented by AI.
Many nations lack the domestic infrastructure to build sovereign artificial intelligence models, forcing them to rely on AI ecosystems developed by foreign tech giants. This creates dependency, transforming commercial software agreements into national security risks. As AI models function as black boxes hosted on external cloud servers, client states have zero visibility into the underlying source code. This exposes them to structural vulnerabilities, such as digital backdoors, intentional data exfiltration, or sudden supply-chain termination. If geopolitical tensions flare, a foreign provider can simply cut off access to the cloud infrastructure, instantly blinding a nation’s automated logistical, banking, or administrative networks.
Following international sanctions stemming from the war in Ukraine, major Western tech giants such as Microsoft, Amazon Web Services (AWS), Google Cloud, and enterprise software giant SAP, systematically cut off access to their cloud platforms in Russia. Tens of thousands of businesses and organisations were given strict deadlines before their data access was permanently terminated. Amidst the chaos, businesses were forced to migrate to inferior domestic software alternatives.
Another stark example of strategic supply-chain termination, is the US using export controls to cripple its adversaries’ AI capabilities. Washington forced Dutch firm Advanced Semiconductor Materials Lithography (which monopolises advanced chip-lithography machines) and the Taiwan Semiconductor Manufacturing Company (the world’s largest advanced contract chipmaker) to instantly halt sales and servicing to Chinese tech companies and data centres. Consequently, nations dependent on Western-licensed hardware were frozen out of the computing power required to build or maintain cutting-edge AI models. It exposed the extreme risk of relying on a supply chain controlled by a foreign superpower.
Governments with constrained budgets must balance the exorbitant cost of investing in AI defence capabilities against immediate domestic needs like healthcare, education, and economic development. AI infrastructure requires massive capital investments in high-performance data centres, microchips, and specialised tech talent. Funding such systems starves essential public services. But to focus resources entirely on social infrastructure creates compounding military risks.
This leaves developing countries trapped in a brutal financial tug-of-war. For example, Kenya recently had to choose between spending its limited cash to fight a massive wave of cyberattacks, or funding schools, hospitals, and food amidst public protests over the high cost of living. If a government picks cyber-defence, its citizens may riot over the lack of public services. But if it ignores the cyber threats, hackers can instantly freeze the country’s banks and power grids. This leaves poorer nations in a dangerous loop: they cannot afford to buy modern AI defences, but they cannot afford to ignore them either. Truly, modern AI-driven rearmament forces developing economies into a destabilising financial paradox.
According to the World Economic Forum’s Global Risks reports, mis- and disinformation are now ranked among the highest short-term global threats precisely because they allow cash-strapped or isolated regimes to strike at the societal core of democratic nations for pennies on the dollar.
Imagine if a bully didn’t have to fight you physically, but could instead instantly whisper a different, perfectly tailored lie into the ear of every kid in school to make them turn on each other. That is exactly what AI-driven information warfare does on a global scale.
By using advanced AI tools, bad actors or rival countries can create incredibly realistic fake videos, audio clips, and social media posts for almost zero cost. Instead of trying to convince everyone of one big lie, they create a digital fog of thousands of small lies designed to target specific arguments people are already having. This makes it impossible for citizens to agree on what is actually real.
While big, wealthy countries have the money and technology to build digital shields to spot and flag these fakes, smaller or less-developed nations often do not. They might not have strong local news stations to double-check the facts, or the right laws to police social media networks. As a result, an attacker can cheaply throw an entire country’s elections or government into total chaos without ever using a real weapon.
Smaller nations face severe regulatory and governance challenges in the age of AI, primarily operating as rule-takers rather than rule-makers. As global frameworks and compliance standards are dictated almost entirely by major powers and supranational bodies like the European Union or NATO, smaller states are forced to adopt external regulations that may not align with their domestic interests. Further, politically fragile states frequently lack the internal institutional capacity and legal frameworks required to regulate and secure AI within their own national defence sectors, leaving them structurally dependent on foreign superpowers.
The idea of introducing thinking machines into war is not new, and attempts have been made by militaries since World War II with little result. Then, innovations in microchips made it possible to introduce microprocesses into military weaponry. This resulted in precision guided munitions that could hit targets on their own once fired but also in systems that could fire automatically. Many US-built legacy systems, such as the Navy’s Close-In Weapon System (CIWS), smart anti-ship mines, and the Army’s Patriot Air Defence System, can engage targets autonomously once activated. Yet, none contain AI, and no one would accuse them of “thinking”. Their logic is entirely predictable, and they operated for decades without triggering global alarm.
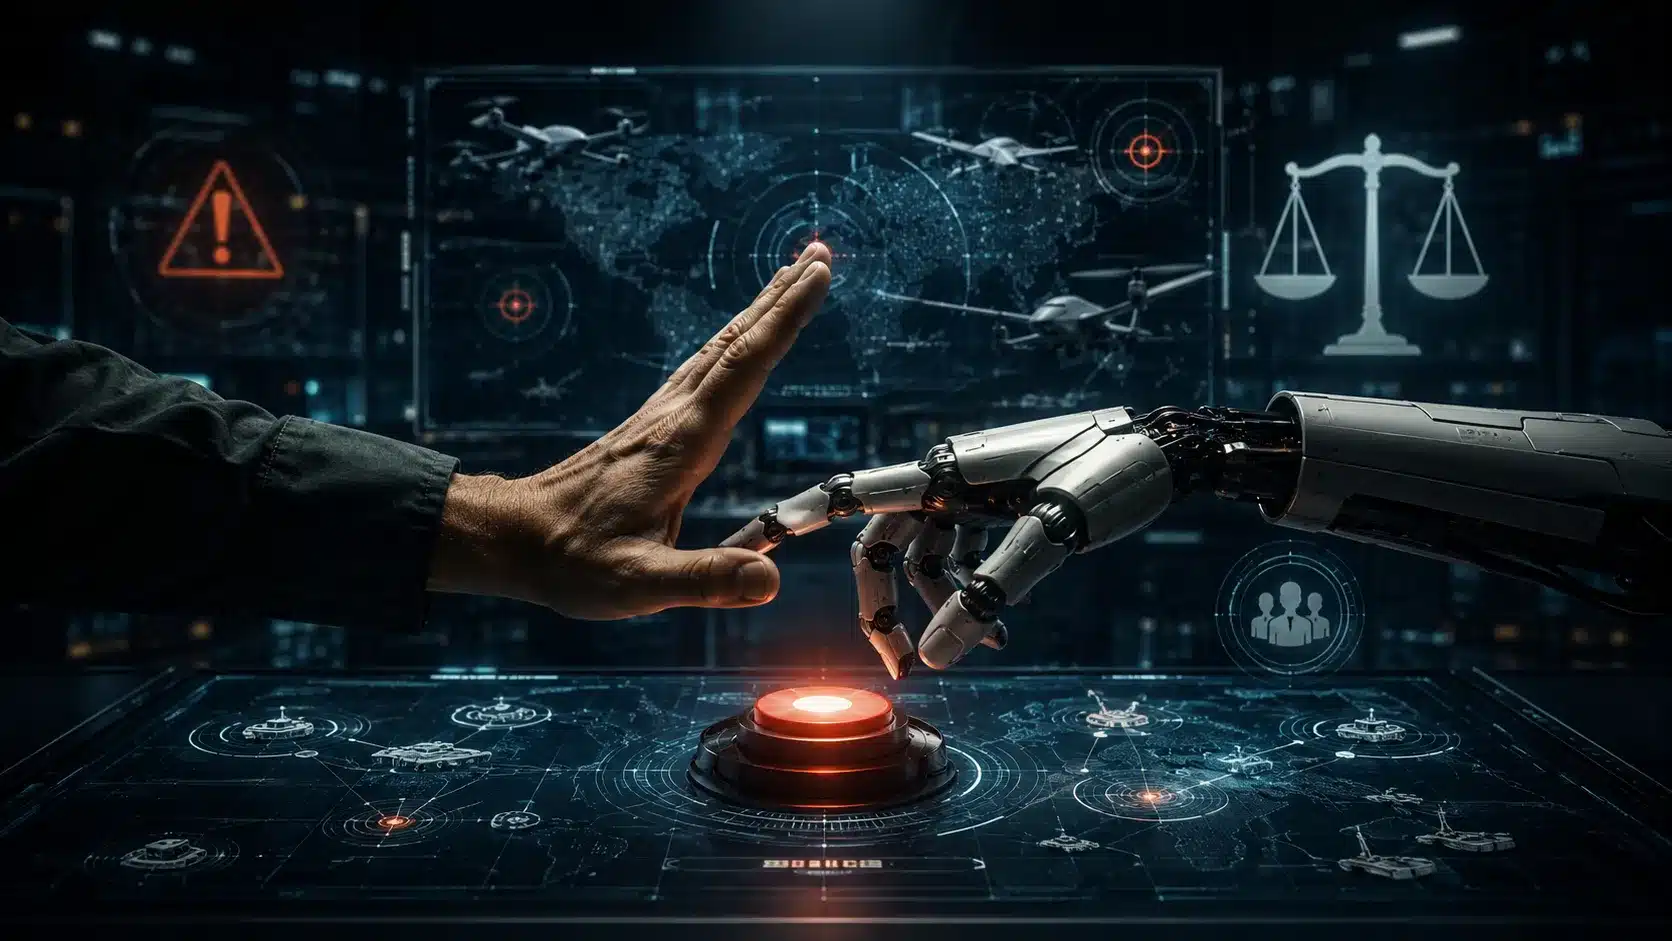
Now, something has changed. The inclusion of AI into military systems has shifted the paradigm from mere automation to true machine autonomy, enabling weapons to select, track, and engage targets using algorithms that operate beyond direct human oversight and predictability. This is immoral and a grave threat to national and global security. As algorithms are incapable of comprehending the value of human life they should never be empowered to decide who lives or dies.
The United Nations Secretary General António Guterres agrees that “machines with the power and discretion to take lives without human involvement are politically unacceptable, morally repugnant and should be prohibited by international law.”
Allowing algorithms to decide when to use lethal force also raises significant questions about who is ultimately responsible and accountable.
What’s scary is experts – including the heads of OpenAI and Google DeepMind – have warned that Artificial intelligence could lead to the extinction of humanity. Dozens have supported a statement published on the webpage of the Centre for AI Safety.
The Centre for AI Safety website suggests a number of possible disaster scenarios:
These scenarios highlight the central paradox of advanced AI: the very technology designed to maximize human efficiency possesses the latent capacity to render humanity obsolete. Far from mere science fiction, these warnings from the industry’s own pioneers underscore that the window for preventing systemic catastrophe is rapidly closing.
© 2026 Suppiah & Partners. All rights reserved. The contents of this newsletter are intended for informational purposes only and do not constitute legal advice.
Quoted by The Star on 18 June 2026
by Martin Carvalho, Ragananthini Vethasalam and Divya Theresa Ravi
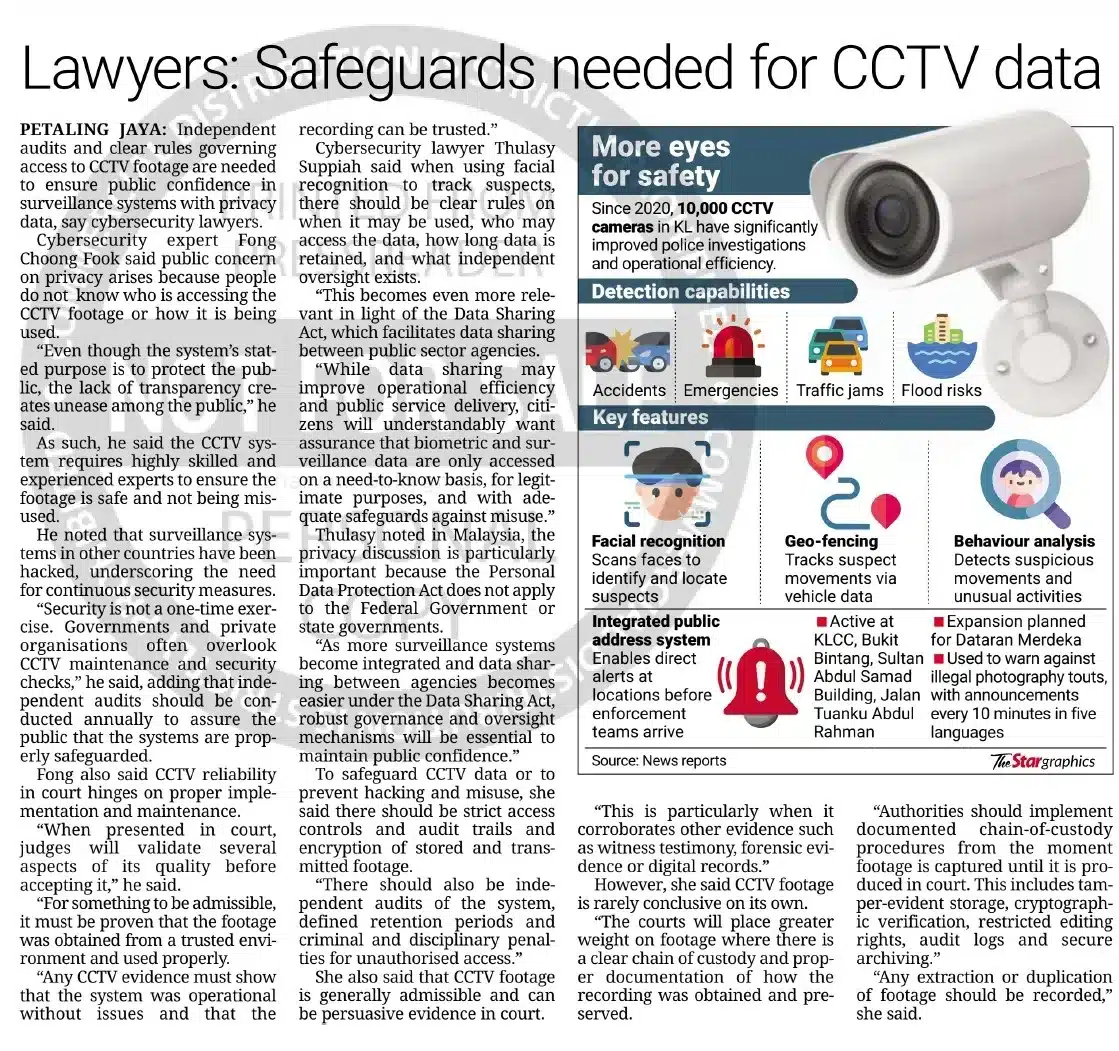
© 2026 Suppiah & Partners. All rights reserved. The contents of this newsletter are intended for informational purposes only and do not constitute legal advice.
Quoted by The Star on 22 May 2026
by Thulasy Suppiah, Managing Partner
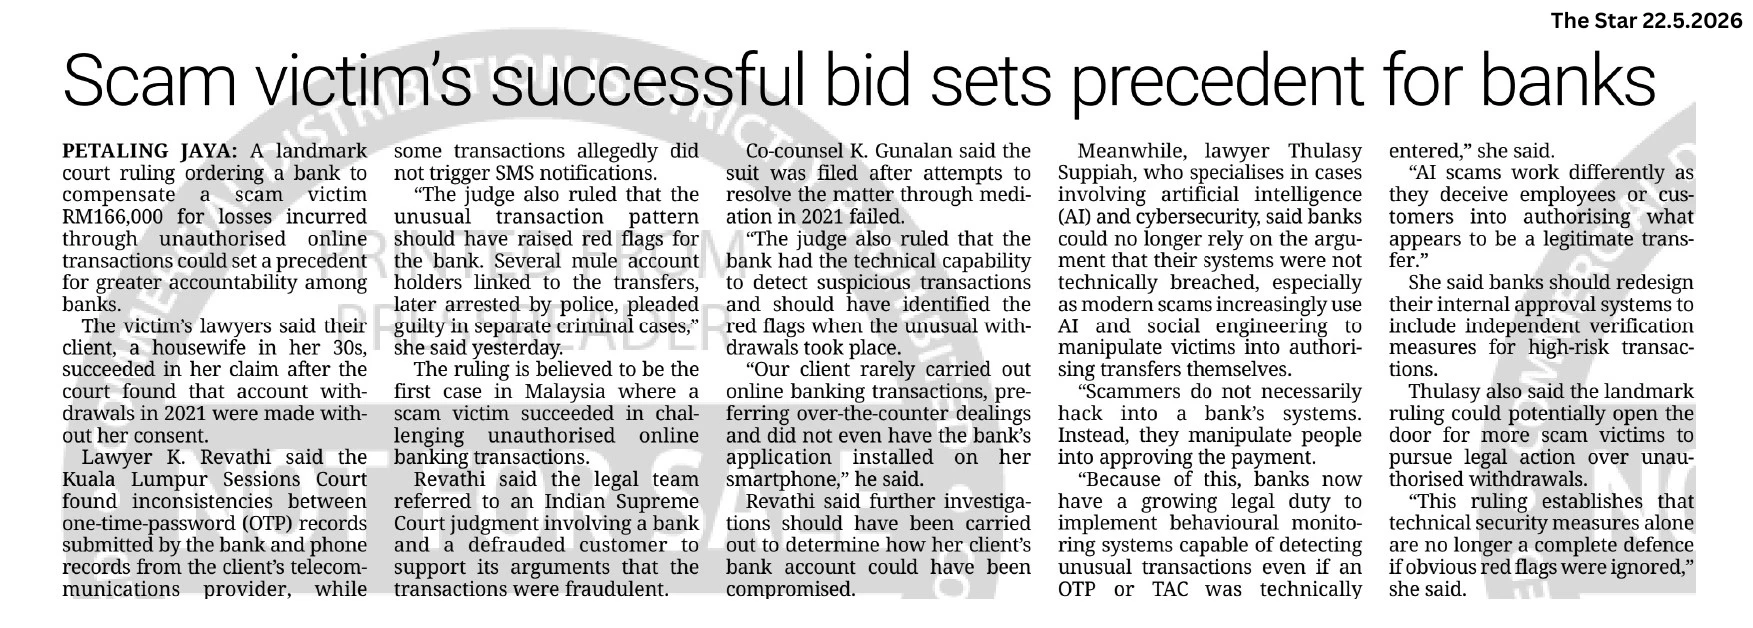
© 2025 Suppiah & Partners. All rights reserved. The contents of this newsletter are intended for informational purposes only and do not constitute legal advice.
Published by The Star on 20 May 2026
By Thulasy Suppiah, Managing Partner of Suppiah & Partners
The recent Sessions Court ruling ordering a local bank to pay RM166,000 for failing to monitor anomalous transactions represents a critical inflection point for corporate governance in Malaysia. By holding the institution liable for ignoring sudden, uncharacteristic account activity, the court effectively dismantled the legacy defence that merely having a secure system—such as sending automated SMS alerts—absolves an organisation of its duty of care.
The ruling sets a clear legal baseline: financial institutions cannot remain passive when faced with glaring transactional anomalies. It reinforces the expectation that financial compliance requires active, intelligent monitoring of escalation triggers, particularly when a transaction drastically deviates from established customer behaviour.
However, if our institutions are currently facing legal liability for missing traditional, rudimentary anomalies, they are alarmingly exposed to the incoming wave of AI-driven financial manipulation. What used to be neatly divided into IT risk versus finance risk is now one combined problem. Cybersecurity and financial compliance can no longer sit in separate rooms.
AI does not necessarily create new categories of fraud; it amplifies existing ones with devastating precision. The 2024 Arup incident, where a multinational engineering firm lost US$25mil after an employee transferred funds based on a deepfake video call with fabricated “senior management,” serves as the global anchor case. It proves an uncomfortable reality: we can no longer trust the channel. Relying on email authenticity, or even live video confirmation, is now an outdated assumption.
Furthermore, AI enables virtually undetectable fraud at scale. Instead of a single large, suspicious transfer, malicious actors can execute hundreds of micro-transactions over time. In this modern “One Cent Thief” scenario, each transaction sits comfortably below automated detection limits and approval thresholds, yet aggregates into significant corporate losses.
This is where our current regulatory frameworks face a critical gap. The Cybersecurity Act 2024 provides a strong foundation for strengthening system resilience and reporting breaches. However, AI introduces a fundamentally different risk. It does not necessarily hack the system; rather, it manipulates how human decisions are made. While current cybersecurity laws protect the infrastructure, they do not fully address the deception embedded within the financial workflow itself.
To survive this shift, corporate boards and audit committees must recognise that the answer is not simply telling employees to “be careful.” Financial approval systems must be actively redesigned to withstand deception. High-risk actions—such as large payments, urgent transfers, or changes to vendor bank details—must trigger mandatory, independent, out-of-band verification using pre-approved contact channels.
Equally critical is the human factor. Fraud often succeeds not because a policy does not exist, but because an employee is pressured by urgency or perceived authority into bypassing it. Corporate culture must empower people to pause, question, and escalate suspicious, time-sensitive instructions. Crucially, no employee should ever be penalised for slowing down a transaction to exercise independent judgment.
The future of financial security is not just building stronger firewalls. It is disciplined human decision-making, better audit trails, and structured verification built directly into financial processes. As the recent court ruling demonstrates, the expectation of accountability is not new. The law is simply evolving to demand that our internal controls are robust enough to manage exactly how decisions are made and acted upon.
© 2025 Suppiah & Partners. All rights reserved. The contents of this newsletter are intended for informational purposes only and do not constitute legal advice.
REACH US
SUPPIAH & PARTNERS
(Formerly Law Office of Suppiah)
NAVIGATION
ARTICLES